

 [PC-DOS] HEROQUEST by Gremlin (1991) REMASTERED, - Modding, Bugfixing e Traduzione ITA/ESP devlog |

Benvenuto Visitatore(Log In|Registrati)
  |
 11 Feb 2024, 22:53
Messaggio
#401
|
|
  Gruppo: OldGamer Messaggi: 2.695 Iscritto il: 15 September 17 Da: España Utente Nr.: 21.627 SO Sono un BOT, cancellami l'account  |
Solo leggerti mi stressa. Puoi, possiamo sempre chiedere aiuto ai miei elfi.
|
 |
 
|


|
11 Feb 2024, 23:42
Messaggio
#402
|
|
|
Gruppo: OldGamer Messaggi: 2.695 Iscritto il: 15 September 17 Da: España Utente Nr.: 21.627 SO Sono un BOT, cancellami l'account |
Sto spostando del codice nel file .bin e leggo dei testi che non riconosco, non so se sono disattivati o non li ricordo, ma sto per giocare il gioco nella sua versione originale per assicurarmi che non sia un bug nella traduzione ufficiale in spagnolo. Questi sono i testi:
-THE CHAOS WARRIORDROPS THE ORCS BANEA QUEST WEAPON (IL GUERRIERO DEL CAOS FA CADERE L'ARMA DELLA MISSIONE BANEA DEGLI ORCHI) -AS YOU ENTER THE WITCH LORDCURSES YOU AND DISAPPEARSAMIDST A HOWLING TEMPEST (APPENA ENTRI IL SIGNORE DELLE STREGHE TI MALEDICE E SCOMPARE IN MEZZO A UNA TEMPESTA ULULANTE) |
|
|
|
|
12 Feb 2024, 08:47
Messaggio
#403
|
|
  Gruppo: SMod Messaggi: 14.544 Iscritto il: 20 January 06 Da: Bologna Utente Nr.: 2.653 Entropologo part-time BGE AG: Indy3 Arcade: Silpheed Free Roaming: Shadow of the Colossus RTS: Praetorians Playing Magari... SO Windows7 OGI Supporter |
CITAZIONE (raul @ 11 Feb 2024, 23:42)  -THE CHAOS WARRIORDROPS THE ORCS BANEA QUEST WEAPON (IL GUERRIERO DEL CAOS FA CADERE L'ARMA DELLA MISSIONE BANEA DEGLI ORCHI) questo l'ho visto, esce quando sconfiggi un guerrirero del caos nella quest "il bastione del caos" CITAZIONE -AS YOU ENTER THE WITCH LORDCURSES YOU AND DISAPPEARSAMIDST A HOWLING TEMPEST (APPENA ENTRI IL SIGNORE DELLE STREGHE TI MALEDICE E SCOMPARE IN MEZZO A UNA TEMPESTA ULULANTE) questa anche io non l'ho mai trovata. -------------------- |
|
|
|


|
12 Feb 2024, 15:34
Messaggio
#404
|
|
|
Gruppo: OldGamer Messaggi: 2.695 Iscritto il: 15 September 17 Da: España Utente Nr.: 21.627 SO Sono un BOT, cancellami l'account |
Interessante, la missione che citi è la spada per uccidere gli orchi, conosciuta in Spagna come la "rovina dell'orco" e c'è già un testo che vi fa riferimento, ma comunque il testo che dico io cita un'arma da inseguimento. Dice quanto segue:
"EL GUERRERO DEL CAOS DEJA CAER EL VENENO DE ORCA,UN ARMA DE RASTREO" "IL GUERRIERO DEL CAOS LASCIA CADERE IL VELENO DELL'ORCO, UN'ARMA DA TRACCIAMENTO." 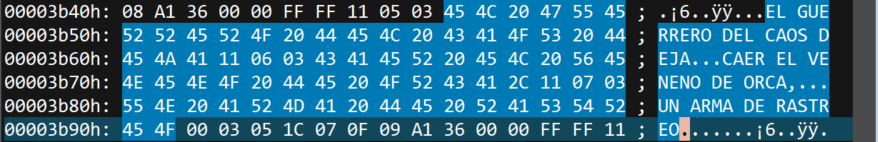 Questo testo vi suona familiare o è stato duplicato? E se è stato duplicato, cosa diavolo hanno sostituito al testo corretto? Messaggio modificato da raul il 12 Feb 2024, 16:07 |
|
|
|
|
12 Feb 2024, 15:42
Messaggio
#405
|
|
|
Gruppo: OldGamer Messaggi: 2.695 Iscritto il: 15 September 17 Da: España Utente Nr.: 21.627 SO Sono un BOT, cancellami l'account |
Mistero risolto, il testo è duplicato e nella traduzione spagnola hanno deciso di cambiare il secondo testo duplicato con qualcosa che solo l'alcol potrebbe spiegare.
Avete già visto questo testo duplicato? Prima di cancellarlo e liberare byte, voglio essere sicuro di non aver cancellato qualcosa di importante. 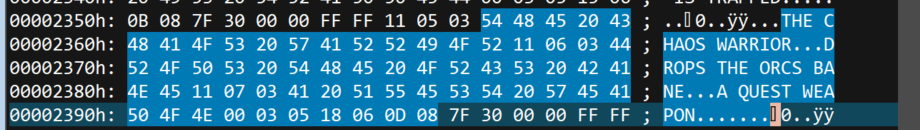 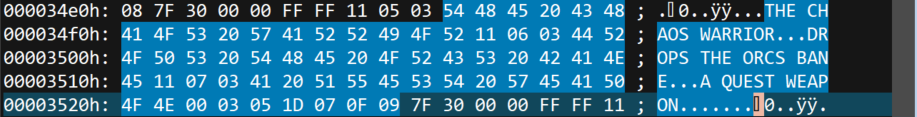 Messaggio modificato da raul il 12 Feb 2024, 15:45 |
|
|
|
|
12 Feb 2024, 16:58
Messaggio
#406
|
|
|
Gruppo: SMod Messaggi: 14.544 Iscritto il: 20 January 06 Da: Bologna Utente Nr.: 2.653 Entropologo part-time BGE AG: Indy3 Arcade: Silpheed Free Roaming: Shadow of the Colossus RTS: Praetorians Playing Magari... SO Windows7 OGI Supporter |
CITAZIONE (raul @ 12 Feb 2024, 15:42) Mistero risolto, il testo è duplicato e nella traduzione spagnola hanno deciso di cambiare il secondo testo duplicato con qualcosa che solo l'alcol potrebbe spiegare. Avete già visto questo testo duplicato? Prima di cancellarlo e liberare byte, voglio essere sicuro di non aver cancellato qualcosa di importante. Devo verificare ma sono sempre d'accordo a liberare spazio soprattutto quando i testi sono identici. Basta cambiare il puntatore e metterlo uguale all'altro. -------------------- |
|
|
|
|
12 Feb 2024, 18:31
Messaggio
#407
|
|
|
Gruppo: OldGamer Messaggi: 2.695 Iscritto il: 15 September 17 Da: España Utente Nr.: 21.627 SO Sono un BOT, cancellami l'account |
Sì, è stata la prima cosa che ho fatto, ma trovo così strano che ci siano così tanti testi duplicati che volevo essere sicuro, non hanno alcun senso. Indagherò sull'altro testo.
|
|
|
|
|
12 Feb 2024, 22:16
Messaggio
#408
|
|
|
Gruppo: SMod Messaggi: 14.544 Iscritto il: 20 January 06 Da: Bologna Utente Nr.: 2.653 Entropologo part-time BGE AG: Indy3 Arcade: Silpheed Free Roaming: Shadow of the Colossus RTS: Praetorians Playing Magari... SO Windows7 OGI Supporter |
CITAZIONE (raul @ 12 Feb 2024, 18:31) Sì, è stata la prima cosa che ho fatto, ma trovo così strano che ci siano così tanti testi duplicati che volevo essere sicuro, non hanno alcun senso. Indagherò sull'altro testo. Immagino tu lo sappia già, se vuoi testarlo in fretta l'ammazzaorchi ce l'ha il guerriero del caos nella stanza centrale (facilmente raggiungibile da un elfo con attraversa la roccia dalla stanza iniziale). -------------------- |
|
|
|
|
12 Feb 2024, 22:34
Messaggio
#409
|
|
|
Gruppo: OldGamer Messaggi: 2.695 Iscritto il: 15 September 17 Da: España Utente Nr.: 21.627 SO Sono un BOT, cancellami l'account |
Immagino che sia colpa del traduttore? Quello che voglio cercare è l'altro testo:
-AS YOU ENTER THE WITCH LORDCURSES YOU AND DISAPPEARSAMIDST A HOWLING TEMPEST (APPENA ENTRI IL SIGNORE DELLE STREGHE TI MALEDICE E SCOMPARE IN MEZZO A UNA TEMPESTA ULULANTE) Si suppone che, secondo le missioni del gioco da tavolo, si trovi nelle sale della morte, ma ho giocato tutto nella versione originale e niente. 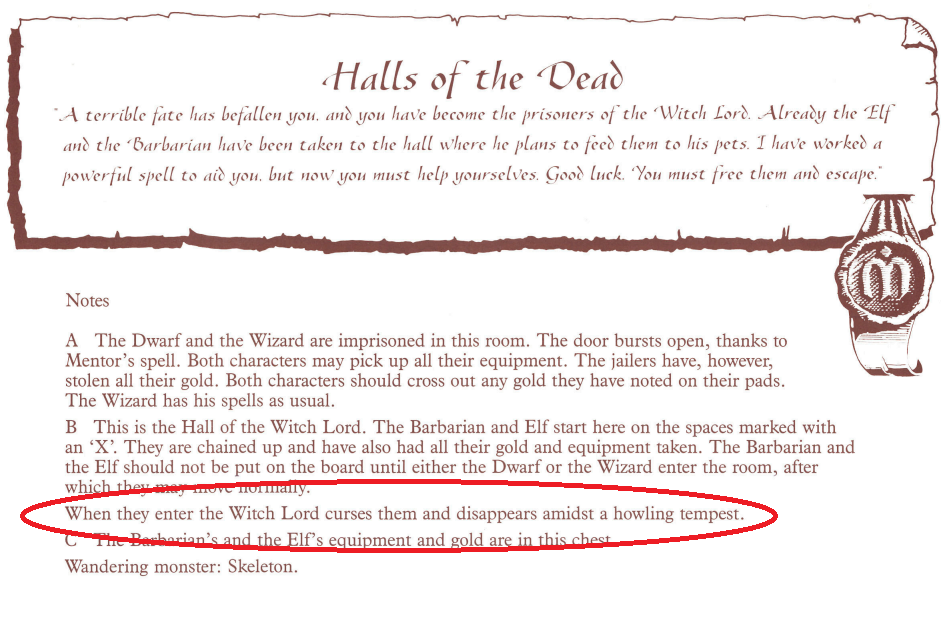 La stanza non esiste nemmeno nel gioco. 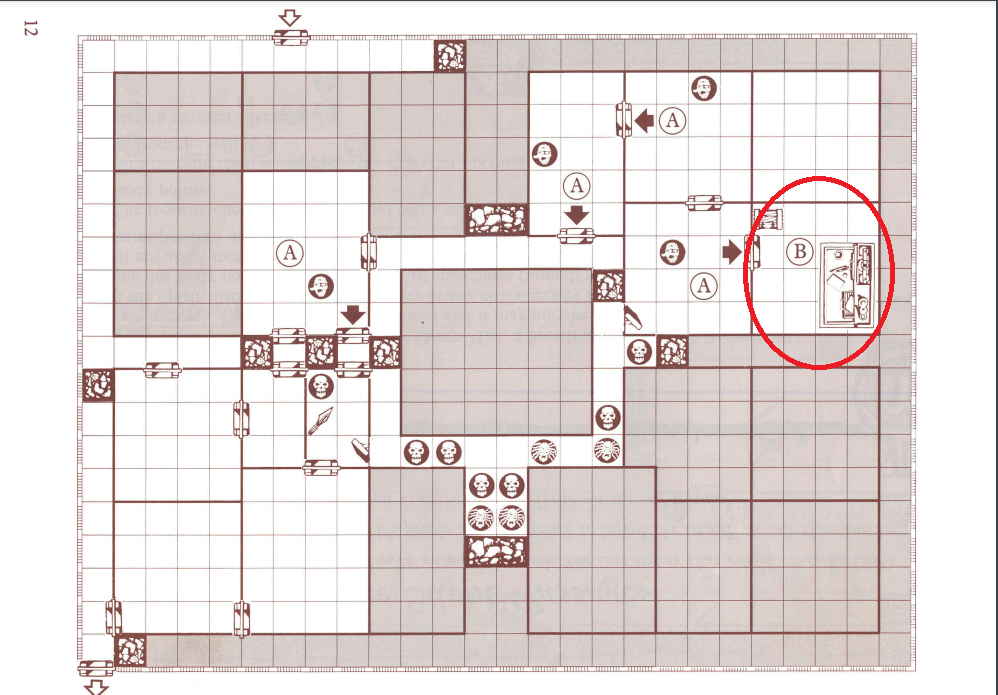
Messaggio modificato da raul il 12 Feb 2024, 22:43 |
|
|
|
|
12 Feb 2024, 23:25
Messaggio
#410
|
|
|
Gruppo: OldGamer Messaggi: 2.695 Iscritto il: 15 September 17 Da: España Utente Nr.: 21.627 SO Sono un BOT, cancellami l'account |
Il labirinto di melar:
Errore riscontrato: si tratta di un banco da alchimista e non di un camino. 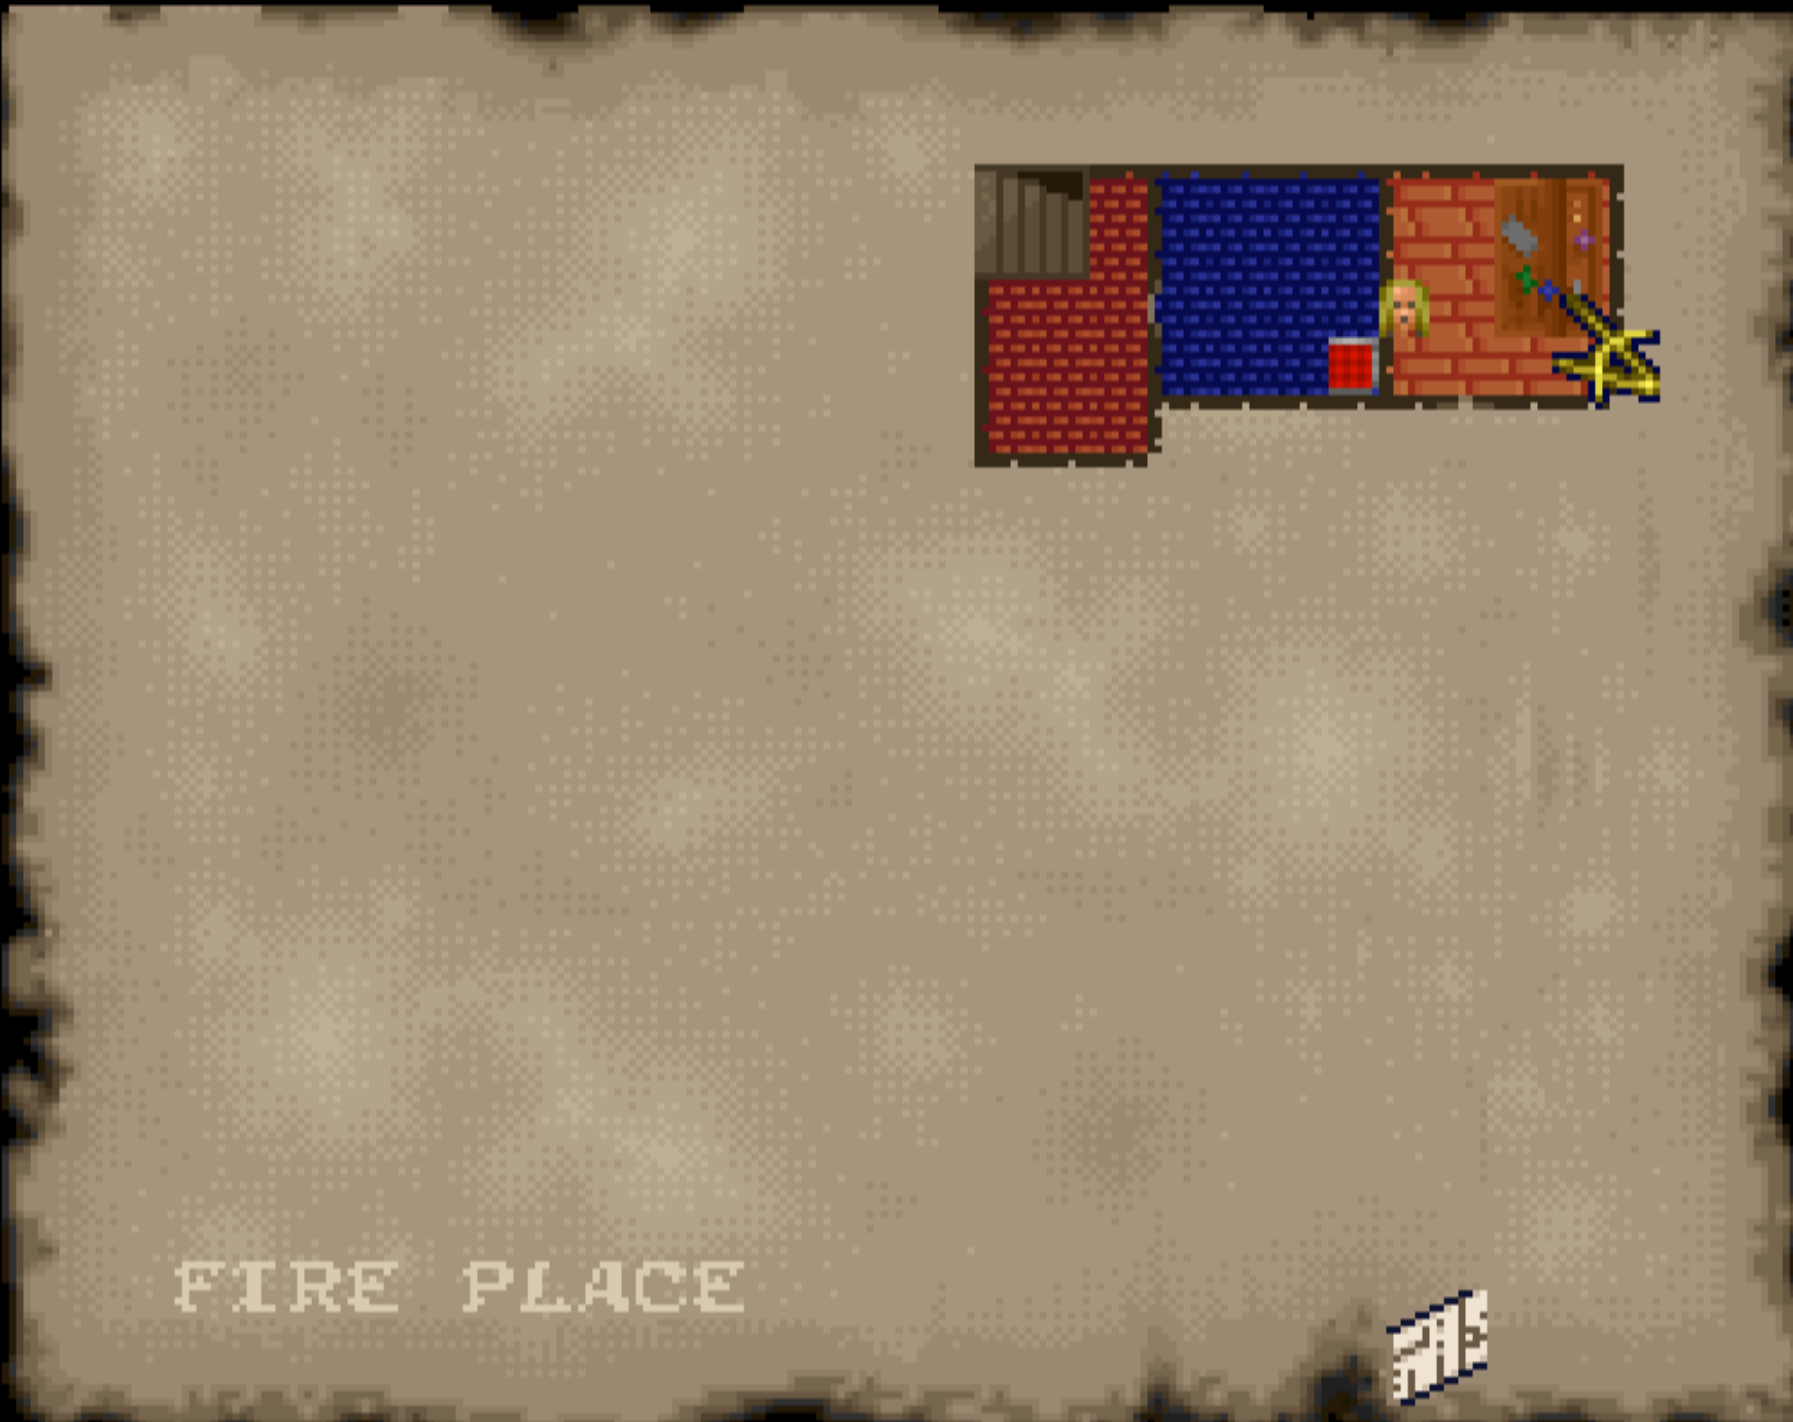 dove sarà il vero camino? C'è una cosa che non mi torna. Giuro e spergiuro di aver visto un camino con il nome giusto, quindi non è impossibile che si tratti di un bug in cui il camino e la banca di alquisma sono identificati con lo stesso nome. Messaggio modificato da raul il 13 Feb 2024, 00:19 |
|
|
|
|
13 Feb 2024, 02:02
Messaggio
#411
|
|
|
Gruppo: SMod Messaggi: 14.544 Iscritto il: 20 January 06 Da: Bologna Utente Nr.: 2.653 Entropologo part-time BGE AG: Indy3 Arcade: Silpheed Free Roaming: Shadow of the Colossus RTS: Praetorians Playing Magari... SO Windows7 OGI Supporter |
I DID IT!
All I had to do was study some assembly! YUCK! The nightmare was to translate the code into opcodes. Never did that but thanks to stackoverflow and a mini guide I've found, I was able to sort it out. I used two different apporaches. According to the original code posted here, I have only 17 bytes to work with. This is the original way the programmers decided to put to zero the 5 bytes of the inventory (per hero): CODICE 01EF:8750 C7066E460000 mov word [466E],0000 ds:[466E]=0000 01EF:8756 C70670460000 mov word [4670],0000 ds:[4670]=FF14 01EF:875C C606724600 mov byte [4672],00 ds:[4672]=000F We have to put to zero 9 bytes so the easiest way would be to replicate the same trick adding two more lines, but we cannot add more code since 17 bytes is what we have. Adding the two lines would require 12 more bytes of space. This approach was not viable. So I used cx registry that was initialized to zero by the previous command and copied it's content into 4 contiguous locations CODICE 01EF:8750 890E6F46 mov [466F],cx ds:[466F]=0000 01EF:8754 890E7146 mov [4671],cx ds:[4671]=0000 01EF:8758 890E7346 mov [4673],cx ds:[4673]=0000 01EF:875C 890E7546 mov [4675],cx ds:[4675]=0000 01EF:8760 90 nop 16 bytes used plus a "no operation" code to fill the gap. With this approach I could put to zero only 8 bytes, and not 9. It worked, everything was correctly wiped out but the elf and mage retained one spell each. So, no-go. the new approach it was a bit tricky but worked like a charm: use a loop to wipe 9 bytes in sequence incrementing the pointer address. this is the code I wrote: CODICE mov cx, 9 <--- Set CX to 9 for the loop mov di, 466Eh <--- Load the memory address into DI barbarian: <--- loop label mov byte [di], 0 <--- Set to zero the byte at the memory address pointed to by DI inc di <--- Move to the next memory address loop barbarian <--- Decrement CX and loop to barbarian label if CX is not zero converted into opcodes and disassembled by dosbox debug: CODICE 01EF:8750 B90900 mov cx,0009 01EF:8753 BF6E46 mov di,466E 01EF:8756 C60500 mov byte [di],00 ds:[DD78]=3838 01EF:8759 47 inc di 01EF:875A E2FA loop 00008756 ($-6) 01EF:875C 90 nop 01EF:875D 90 nop 01EF:875E 90 nop 01EF:875F 90 nop 01EF:8760 90 nop 12 bytes used for the code plus 5 bytes used byt the "no operation" opcodes. So to correctly modify the (uncompressed) QUEST.EXE: CODICE (Barbarian) search for: C7066E460000C70670460000C606724600 overwrite with: B90900BF6E46C6050047E2FA9090909090 (Dwarf) search for: C70688460000C7068A460000C6068C4600 overwrite with: B90900BF8846C6050047E2FA9090909090 (Elf) search for: C706A2460000C706A4460000C606A64600 overwrite with: B90900BFA246C6050047E2FA9090909090 (Mage) search for: C706BC460000C706BE460000C606C04600 overwrite with: B90900BFBC46C6050047E2FA9090909090 That was tough. EDIT, OPTIMIZED CODE TO FREE SPACE FOR OTHER NEW CODE (GENIE.REVEAL DELETION SPELL FUNCTION): CODICE ottimizzazione codice da 01EF:8745 a 87B5 01EF:8745 BE6E46 mov si,466E 01EF:8748 BF9F4A mov di,4A9F 01EF:874B B105 mov cl,05 01EF:874D F3A4 repe movsb 01EF:874F B109 mov cl,09 01EF:8751 BF6E46 mov di,466E 01EF:8754 C60500 mov byte [di],00 ds:[7507]=3901 01EF:8757 47 inc di 01EF:8758 E2FA loop 00008754 ($-6) 01EF:875A BE8846 mov si,4688 01EF:875D BFA44A mov di,4AA4 01EF:8760 B105 mov cl,05 01EF:8762 F3A4 repe movsb 01EF:8764 B109 mov cl,09 01EF:8766 BF8846 mov di,4688 01EF:8769 C60500 mov byte [di],00 ds:[7507]=3901 01EF:876C 47 inc di 01EF:876D E2FA loop 00008769 ($-6) 01EF:876F BEA246 mov si,46A2 01EF:8772 BFA94A mov di,4AA9 01EF:8775 B105 mov cl,05 01EF:8777 F3A4 repe movsb 01EF:8779 B109 mov cl,09 01EF:877B BFA246 mov di,46A2 01EF:877E C60500 mov byte [di],00 ds:[7507]=3901 01EF:8781 47 inc di 01EF:8782 E2FA loop 0000877E ($-6) 01EF:8784 BEBC46 mov si,46BC 01EF:8787 BFAE4A mov di,4AAE 01EF:878A B105 mov cl,05 01EF:878A B105 mov cl,05 01EF:878C F3A4 repe movsb 01EF:878E B109 mov cl,09 01EF:8790 BFBC46 mov di,46BC 01EF:8793 C60500 mov byte [di],00 ds:[7507]=3901 01EF:8796 47 inc di 01EF:8797 E2FA loop 00008793 ($-6) 01EF:8799 EB1A jmp short 000087B5 ($+1a) (down) 01EF:879B 90 nop 01EF:879C 90 nop 01EF:879D 90 nop 01EF:879E 90 nop 01EF:879F 90 nop 01EF:87A0 90 nop 01EF:87A1 90 nop 01EF:87A2 90 nop 01EF:87A3 90 nop 01EF:87A4 90 nop 01EF:87A5 90 nop 01EF:87A6 90 nop 01EF:87A7 90 nop 01EF:87A8 90 nop 01EF:87A9 90 nop 01EF:87AA 90 nop 01EF:87Ab 90 nop 01EF:87AB 90 nop 01EF:87AC 90 nop 01EF:87AD 90 nop 01EF:87AE 90 nop 01EF:87AF 90 nop 01EF:87B0 90 nop 01EF:87B2 90 nop 01EF:87B3 90 nop 01EF:87B4 90 nop CITAZIONE at offset 0x8B65 replace the subsequent 112 (0x70) bytes with these:
BE6E46BF9F4AB105F3A4B109BF6E46C6050047E2FABE8846BFA44AB105F3A4B109BF8846C6050047 E2FABEA246BFA94AB105F3A4B109BFA246C6050047E2FABEBC46BFAE4AB105F3A4B109BFBC46C6050 047E2FAEB1A9090909090909090909090909090909090909090909090909090 -------------------- |
|
|
|
|
13 Feb 2024, 02:27
Messaggio
#412
|
|
|
Gruppo: SMod Messaggi: 14.544 Iscritto il: 20 January 06 Da: Bologna Utente Nr.: 2.653 Entropologo part-time BGE AG: Indy3 Arcade: Silpheed Free Roaming: Shadow of the Colossus RTS: Praetorians Playing Magari... SO Windows7 OGI Supporter |
Here is the code in action.
While running the code in the "code overview", keep an eye on the "data overview", starting from top left you will see the bytes go to zero. In the "registry overview" see the ESI and EDI registry change while CX decrements from 9 to 0 according to the code below.  loopcode_quest5_bugfix.gif ( 1.52mb )
Numero di download: 20 -------------------- |
|
|
|
|
13 Feb 2024, 06:37
Messaggio
#413
|
|
|
Gruppo: OldGamer Messaggi: 2.695 Iscritto il: 15 September 17 Da: España Utente Nr.: 21.627 SO Sono un BOT, cancellami l'account |
 Spero che abbiate una soluzione facile da implementare in esadecimale, qualcosa mi dice che non si tratta solo di modificare il codice. Messaggio modificato da raul il 13 Feb 2024, 06:38 |
|
|
|
|
13 Feb 2024, 09:45
Messaggio
#414
|
|
|
Gruppo: SMod Messaggi: 14.544 Iscritto il: 20 January 06 Da: Bologna Utente Nr.: 2.653 Entropologo part-time BGE AG: Indy3 Arcade: Silpheed Free Roaming: Shadow of the Colossus RTS: Praetorians Playing Magari... SO Windows7 OGI Supporter |
CITAZIONE (raul @ 13 Feb 2024, 06:37) Spero che abbiate una soluzione facile da implementare in esadecimale, qualcosa mi dice che non si tratta solo di modificare il codice. Basta seguire le istruzioni dell'ultimo blocco nel post precedente. Cerchi la prima sequenza e la sostituisci con quella sotto, per tutte e 4 le aree. le 4 sostituzioni sono i codici per i 4 eroi, in fila barbaro, nano, elfo, mago. Ora è davvero così semplice. 
-------------------- |
|
|
|
|
13 Feb 2024, 11:44
Messaggio
#415
|
|
 Gruppo: OldGamer Messaggi: 332 Iscritto il: 27 June 14 Utente Nr.: 20.463 BGE Command & Conquer: Tiberian Dawn SO Windows7 |
QUOTE (TheRuler @ 13 Feb 2024, 02:02) I DID IT! All I had to do was study some assembly! YUCK! The nightmare was to translate the code into opcodes. Never did that but thanks to stackoverflow and a mini guide I've found, I was able to sort it out. Nice to see you making your way into actual assembly. It'll make things a lot easier if you can actually see the code and translate it. But generally people don't bother doing that stuff manually; there are tools for that, you know. I know IDA Pro can handle 16 bit code, though if I recall correctly it's pretty bad at connecting links and calls between the different segments in 16-bit (a 32-bit program generally only has one large code segment, but a 16-bit one has many small segments it jumps between). I'm not sure if the free version can do the same, but it seems like it might be worth a shot. Or can you do disassembly of exe files with the DOSBox debugger too? QUOTE (TheRuler @ 13 Feb 2024, 02:02) That was tough. That was also very nicely done! Just a note on using registers: this kind of operation might go wrong if the registers you use are in use, since you are changing their values. If you double-checked on all four cases that both CX and DI are not corrupted by your operation, then everything is okay, but this is only true if they either have the correct value at the end of your operation, or are set to new values in following instructions without being read first. But from your gif, I can see both are immediately set to new values after your operation anyway, so that means they're perfectly safe to use. So if that's true in all 4 cases, everything is perfect, there. However, if you ever have the need to use registers that are in use in the surrounding code, there's a very easy way to prevent them from corrupting: to make a backup of a value in the stack, you simply have to PUSH it before your operation, and then you can POP it out after your operation. You just have to make sure that if you do this with multiple variables, you have to POP them back out in reverse order from how they were pushed in, or you're putting the values back into the wrong register (though this is a pretty efficient way to swap the values of two registers, if you'd ever need that). Push and pop are both 1-byte operations, so it's quite space-efficient too; even in your existing code, you could easily put a push and pop for these two registers and you'd still have a byte left over. In fact, if you'd disassemble an entire function, you'd see that pretty much all functions in a program start with pushing all registers they use and popping them at the end, so they don't corrupt the values they had in the function that calls that one. Well, all except AX, generally, since that acts as the "return value" of the function. Messaggio modificato da Nyerguds il 13 Feb 2024, 12:09 -------------------- Expert on all things Command & Conquer 1. Creator of a bunch of small modding tools.
|
|
|
|
|
13 Feb 2024, 15:24
Messaggio
#416
|
|
|
Gruppo: OldGamer Messaggi: 2.695 Iscritto il: 15 September 17 Da: España Utente Nr.: 21.627 SO Sono un BOT, cancellami l'account |
CITAZIONE (TheRuler @ 13 Feb 2024, 09:45) Ora è davvero così semplice. Non l'ho nemmeno visto perché ero così eccitato. In questo momento vorrei essere inghiottito dalla terra e avere la possibilità di cancellare il messaggio. Lo proverò subito. Come te la cavi con le trappole che non possono essere scoperte quando le cerchi? |
|
|
|
|
13 Feb 2024, 15:45
Messaggio
#417
|
|
|
Gruppo: SMod Messaggi: 14.544 Iscritto il: 20 January 06 Da: Bologna Utente Nr.: 2.653 Entropologo part-time BGE AG: Indy3 Arcade: Silpheed Free Roaming: Shadow of the Colossus RTS: Praetorians Playing Magari... SO Windows7 OGI Supporter |
CITAZIONE (raul @ 13 Feb 2024, 15:24) Come te la cavi con le trappole che non possono essere scoperte quando le cerchi? ancora non ci ho guardato. Credo che per questa settimana ho terminato il tempo da dedicare a questo hobby, ma è nella lista delle cose da fare. Ti andrebbe per cortesia di elencare i bug in sospeso per cui ancora non abbiamo una soluzione o workaround? -------------------- |
|
|
|
|
13 Feb 2024, 15:59
Messaggio
#418
|
|
|
Gruppo: OldGamer Messaggi: 2.695 Iscritto il: 15 September 17 Da: España Utente Nr.: 21.627 SO Sono un BOT, cancellami l'account |
Sì, non preoccupatevi, ho sempre un txt con le attività in sospeso, posso anche inserirne altre che non vi ho detto. Ora lo preparo e lo pubblico.
A proposito, confermo quello che ho detto prima: il banco dell'alchimista e il camino hanno lo stesso nome. 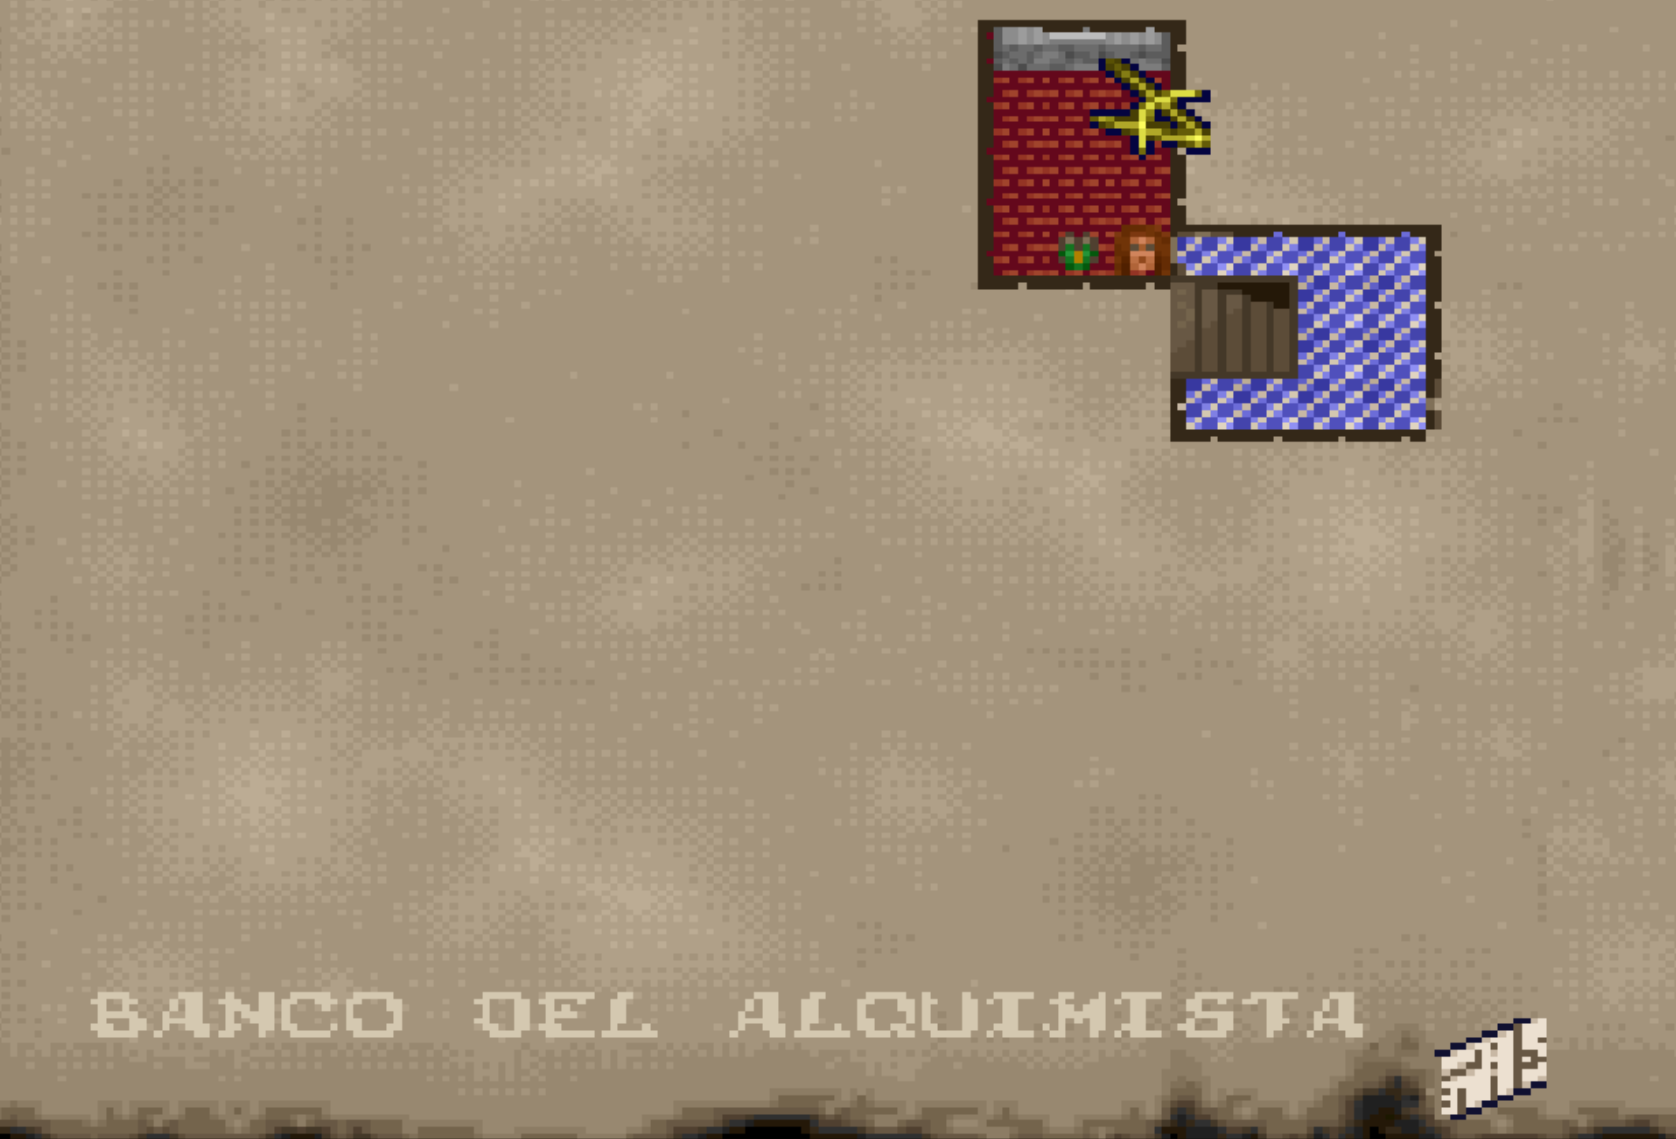
|
|
|
|
|
13 Feb 2024, 16:01
Messaggio
#419
|
|
|
Gruppo: SMod Messaggi: 14.544 Iscritto il: 20 January 06 Da: Bologna Utente Nr.: 2.653 Entropologo part-time BGE AG: Indy3 Arcade: Silpheed Free Roaming: Shadow of the Colossus RTS: Praetorians Playing Magari... SO Windows7 OGI Supporter |
CITAZIONE (Nyerguds @ 13 Feb 2024, 11:44) I'm not sure if the free version can do the same, but it seems like it might be worth a shot. Or can you do disassembly of exe files with the DOSBox debugger too? I am that kind of person that take his time to do things slowly (the reality is that I AM ACTUALLY SLOW because of my limited knowledge in programming). ;-) I actually tried IDA free, I used it in the past but never dove into it to understand how to use it with proficency. Anyway this version does not chew well old 16bit dos code. I have a previous free version 5.8-6.1, I dont recall correctly, that managed 16bit code well. When I use mov word or byte instructions ida always wanted to use 32 addressing instead of 16bit for the operand thus messing up the code and the loop return. Because the well opcoded loop code always returned back 2 byte short! Maybe they dropped the support, don't know. Anyway I did what you thought, I've used dosbox debugger directly to test my code. It was a bit inefficent but worked well. CITAZIONE Just a note on using registers: this kind of operation might go wrong if the registers you use are in use, since you are changing their values. If you double-checked on all four cases that both CX and DI are not corrupted by your operation, then everything is okay, but this is only true if they either have the correct value at the end of your operation, or are set to new values in following instructions without being read first. But from your gif, I can see both are immediately set to new values after your operation anyway, so that means they're perfectly safe to use. So if that's true in all 4 cases, everything is perfect, there. However, if you ever have the need to use registers that are in use in the surrounding code, there's a very easy way to prevent them from corrupting: to make a backup of a value in the stack, you simply have to PUSH it before your operation, and then you can POP it out after your operation. You just have to make sure that if you do this with multiple variables, you have to POP them back out in reverse order from how they were pushed in, or you're putting the values back into the wrong register (though this is a pretty efficient way to swap the values of two registers, if you'd ever need that). Push and pop are both 1-byte operations, so it's quite space-efficient too; even in your existing code, you could easily put a push and pop for these two registers and you'd still have a byte left over. In fact, if you'd disassemble an entire function, you'd see that pretty much all functions in a program start with pushing all registers they use and popping them at the end, so they don't corrupt the values they had in the function that calls that one. Well, all except AX, generally, since that acts as the "return value" of the function. that's very informative Maarten, thank you! I didn't even know what push and pop instructions did, and I actually see them around a lot as you exactly stated! I Simply didn't bother to study them, but now that I am aware of them I will surely pay attention. In fact I was a bit concerned to not mess up the registers so, without a real clue but only a misgiving, I decided to use registers that were already at zero, or used in the same function. As you see I've used DI knowing that it was used just before and it will be used again just after my code. Here is the surrounding lines: CODICE 01EF:8745 BE6E46 mov si,466E
01EF:8748 BF9F4A mov di,4A9F 01EF:874B B90500 mov cx,0005 01EF:874E F3A4 repe movsb 01EF:8750 B90900 mov cx,0009 01EF:8753 BF6E46 mov di,466E 01EF:8756 C60500 mov byte [di],00 ds:[DD78]=3838 01EF:8759 47 inc di 01EF:875A E2FA loop 00008756 ($-6) 01EF:875C 90 nop 01EF:875D 90 nop 01EF:875E 90 nop 01EF:875F 90 nop 01EF:8760 90 nop 01EF:8761 BE8846 mov si,4688 01EF:8764 BFA44A mov di,4AA4 01EF:8767 B90500 mov cx,0005 01EF:876A F3A4 repe movsb -------------------- |
|
|
|
|
13 Feb 2024, 16:10
Messaggio
#420
|
|
|
Gruppo: OldGamer Messaggi: 2.695 Iscritto il: 15 September 17 Da: España Utente Nr.: 21.627 SO Sono un BOT, cancellami l'account |
CITAZIONE (TheRuler @ 13 Feb 2024, 15:45) Ti andrebbe per cortesia di elencare i bug in sospeso per cui ancora non abbiamo una soluzione o workaround? Riposati, te lo sei meritato... 1.-Controllare le trappole che non compaiono quando si cerca "porte e trappole segrete". 2.-Controllare se i camini e i banchi degli alchimisti hanno i loro rispettivi nomi. 3.-Controllare le trappole che si trovano dietro la scatola nella schermata successiva. 4.-Testo "APPENA ENTRI IL SIGNORE DELLE STREGHE TI MALEDICE E SCOMPARE IN MEZZO A UNA TEMPESTA ULULANTE" 5.- .................. Testare gli eroi senza attrezzature .................. ELFO: Beh MAGO: Non esce mai nessuno scudo o teschio BARBARO: ENANO: Messaggio modificato da raul il 13 Feb 2024, 16:35 |
|
|
|
|
13 Feb 2024, 16:25
Messaggio
#421
|
|
|
Gruppo: SMod Messaggi: 14.544 Iscritto il: 20 January 06 Da: Bologna Utente Nr.: 2.653 Entropologo part-time BGE AG: Indy3 Arcade: Silpheed Free Roaming: Shadow of the Colossus RTS: Praetorians Playing Magari... SO Windows7 OGI Supporter |
CITAZIONE (raul @ 13 Feb 2024, 16:10) 1.-Controllare le trappole che non compaiono quando si cerca "porte e trappole segrete". Al momento qui i workaround sono due per due casi diversi: 1. spostare la trappola in un altro posto perché abbiamo visto che su alcune caselle non viene trovata e su altre sì 2. non utilizzare mai l'evento speciale 16 (Chest Trapped, -1 body point) perché non fa trovare passaggi segreti dopo aver cercato tesori, usare invece l'evento 2 (che è uguale) al suo posto che funziona perfettamente. CITAZIONE 2.-Controllare se i camini e i banchi degli alchimisti hanno i loro rispettivi nomi. può capitare che siano stati sovrapposti due oggetti e quando accade il gioco ne mostra solo uno, l'ultimo che viene disegnato. Devo verificarlo nella quest. Ad ogni modo, vedi se per caso fa lo stesso in inglese, perché in italiano non mi pare di essermene mai accorto. Magari è un bug di Spanish.bin. CITAZIONE 3.-Controllare le trappole che si trovano dietro la scatola nella schermata successiva. non ho capito cosa intendi con scatola CITAZIONE 4.- rivedere il testo "AL ENTRAR, EL SEÑOR BRUJO TE MALDICE Y DESAPARECE EN MEDIO DE UNA TORMENTA AULLADORA" ok, segnato. Ho comunque guardato nel codice e il pointer a quella stringa esiste, solo non so ancora quale funzione la fa scattare. Magari è un bug come quell'altro che non faceva vedere lo scroll. la funzione esiste e funziona ma non mostra lo scroll con questo testo. CITAZIONE 5.- .................. Testare gli eroi senza attrezzature .................. Io l'ho già fatto e funziona incredibilmente tutto. Ancora mi stupisco ;-) -------------------- |
|
|
|
|
13 Feb 2024, 16:35
Messaggio
#422
|
|
|
Gruppo: OldGamer Messaggi: 2.695 Iscritto il: 15 September 17 Da: España Utente Nr.: 21.627 SO Sono un BOT, cancellami l'account |
1.- Ci sono ancora altre stanze che presentano questo problema, per questo le ho chiesto se voleva che cercassi tutte le stanze.
2.- Infatti, ho postato uno screenshot della versione originale del gioco. 3.- piastrella per pavimento / griglia per pavimento / quadrato per pavimento 4.- Se necessario, per trovare il gioco completo nella sua versione originale. 5.- ELFO: Beh MAGO: Non esce mai nessuno scudo o teschio BARBARO: Beh ENANO: Non esce mai nessuno scudo o teschio Messaggio modificato da raul il 13 Feb 2024, 17:23 |
|
|
|
|
13 Feb 2024, 17:26
Messaggio
#423
|
|
|
Gruppo: OldGamer Messaggi: 2.695 Iscritto il: 15 September 17 Da: España Utente Nr.: 21.627 SO Sono un BOT, cancellami l'account |
ELFO: Beh
MAGO: Non esce mai nessuno scudo o teschio BARBARO: Beh ENANO: Non esce mai nessuno scudo o teschio Ho controllato e in effetti né il mago né il nano tirano fuori teschi o scudi. Ciò che potrebbe essere importante è che questo si ripropone anche nel resto delle missioni con un personaggio resettato dall'inizio. In pratica si tratta di aver cambiato gli attributi iniziali di default. Messaggio modificato da raul il 13 Feb 2024, 17:28 |
|
|
|
|
13 Feb 2024, 17:33
Messaggio
#424
|
|
|
Gruppo: OldGamer Messaggi: 332 Iscritto il: 27 June 14 Utente Nr.: 20.463 BGE Command & Conquer: Tiberian Dawn SO Windows7 |
QUOTE (TheRuler @ 13 Feb 2024, 16:01) that's very informative Maarten, thank you! I didn't even know what push and pop instructions did, and I actually see them around a lot as you exactly stated! I Simply didn't bother to study them, but now that I am aware of them I will surely pay attention. In fact I was a bit concerned to not mess up the registers so, without a real clue but only a misgiving, I decided to use registers that were already at zero, or used in the same function. As you see I've used DI knowing that it was used just before and it will be used again just after my code. Here is the surrounding lines: Basically you have three types of "memory" to use in a program: the "Heap", the "Stack", and "var" sections in the exe. The "Var" sections act kind of like an extension of the exe file; an exe will have code sections (generally referred to as "text"), hardcoded data sections ("referred to as "data") containing game text and such, and var sections, which in a debugger or disassembler will look the same as a data section, except nothing is filled into them by default. The "heap" is just a bunch of open space, and the program can ask the operating system to reserve X amount of bytes in there, and then you have a pointer, and you know that at that pointer, you can store data with a length of X bytes. If the program is done with that data, it needs to specifically ask the OS to destroy the reservation so the memory is freed up again. The third type, the "stack", is a bit more complex. This is the actual memory that functions work with directly. As the name says, it's a stack of data, so you generally always only access the top of it, either adding to it, or removing from it. Any time you enter a new function, the address of the place that did the call to that function will be pushed onto the stack, so that at the end of a function, when a "retn" is called, the CPU simply has to read that value off the stack to know where to return to. But the stack is used for more than that; when a function has arguments that are needed for calling it, then some of these can be put in AX, BX, CX and DX, but if there are any more, the registers alone won't do the job. In that case, these are also PUSHed onto the stack. Since you can see the current position of the stack in the "SP" (Stack Pointer) register, you can also use SP to retrieve the pushed data from memory. The receiving function knows how many pushed arguments it requires, and has the responsibility of lowering the stack accordingly; you can see such functions will then end with an instruction like "retn 4" to tell the system how many extra bytes to take off the stack along with the return address. And sometimes you'll see how a function subtracts from the stack pointer at the start, and adds that same number again at the end. This is actually how it reserves space for local variables; the space in between the original position and the new one can now be freely used without being affected by other function calls. Now, if you paid attention, you'll probably wonder at this point "wait, but, if it subtracts at the start, won't that overwrite previously-pushed data?" And that's true, but, actually, no. Because I simplified things a bit. See, the stack actually works in reverse: it starts at the end of the available memory, and decreases as it puts in data. This is simply because then the computer can very easily see that when it reaches 0, it's out of memory. For that reason, you'll also see SP go down when you push a value or when you call a function, and go back up when a pop instruction is executed, or when you return from a function. Stack filling downwards:  stack2.png ( 10.31k )
Numero di download: 0 Function reserving space on the stack for local function variables:
stack_vars.png ( 13.15k )
Numero di download: 0(note, these say "ESP" because they were made to showcase this in 32-bit. In 16 bit it's "SP") Messaggio modificato da Nyerguds il 13 Feb 2024, 17:59 -------------------- Expert on all things Command & Conquer 1. Creator of a bunch of small modding tools.
|
|
|
|
|
13 Feb 2024, 17:40
Messaggio
#425
|
|
|
Gruppo: SMod Messaggi: 14.544 Iscritto il: 20 January 06 Da: Bologna Utente Nr.: 2.653 Entropologo part-time BGE AG: Indy3 Arcade: Silpheed Free Roaming: Shadow of the Colossus RTS: Praetorians Playing Magari... SO Windows7 OGI Supporter |
CITAZIONE (raul @ 13 Feb 2024, 17:26) ELFO: Beh MAGO: Non esce mai nessuno scudo o teschio BARBARO: Beh ENANO: Non esce mai nessuno scudo o teschio Ho controllato e in effetti né il mago né il nano tirano fuori teschi o scudi. Ciò che potrebbe essere importante è che questo si ripropone anche nel resto delle missioni con un personaggio resettato dall'inizio. In pratica si tratta di aver cambiato gli attributi iniziali di default. that's very strange. Because I didn't touch 03 and 02 that are the basic defend and attack dice. CODICE BEFORE: 0000:FD1E 00 00 14 FF 0F 00 10 00 02 03 02 AFTER: 0000:FD1E 00 00 00 00 00 00 00 00 00 03 02 Please check the code you changed or send me the quest.exe. You could try finishing the quest anyway and then save the characters into another slot. Then try other quests with those saves. Send me the QUEST.SAV also. -------------------- |
|
|
|
|
1 utenti stanno leggendo questa discussione (1 visitatori e 0 utenti anonimi)
0 utenti:
| Versione Lo-Fi | Oggi è il: 28th October 2026 - 13:42 |